
01 / INVISIBLE THREATS
Retrospective & fileless gaps
EDR/XDR and SIEM alone can't catch every retrospective, fileless or hidden threat.
ATF Quad Engine + AtlantisDeep scanning, artifact collection and retrospective visibility in one workflow.
Defensium unifies hunting, detection, analysis, investigation, response, reporting and management on one on-prem operating surface — so evidence, detection and response never leave the same workflow.

We prove your environment is clean.
Teams must act fast, but a stack of point products scatters artifacts, logs and case context across surfaces — and the burden lands on the analyst. Here's how Defensium closes each gap.
EDR/XDR and SIEM alone can't catch every retrospective, fileless or hidden threat.
Endpoint artifacts, logs and incident context live in different tools.
Analyst hours disappear between alert triage and manual data collection.
Detection, investigation and response run on separate surfaces, so action quality drops.
Performance was the fifth blocker. Teams feared scanning critical servers at all. Defensium's ultra-light agent starts scans on your most critical hosts under strict CPU and RAM limits — so nothing is off-limits.
One operating path from signal to outcome: clearer visibility, faster investigation, more controlled response, and reporting that means something.
Multi-layer scanning and rule-based validation with the ATF Quad Engine.
Prioritization, timeline and evidence context built with Atlantis.
Artifact, telemetry and host relationships in one investigation flow.
Isolate, quarantine, shell, OS Query and playbooks — take action in place.
Investigation summary, auto timeline, scan results and executive output.
Agents, scans, licensing and operations from one platform.
The ATF Quad Engine correlates high-confidence findings across four inputs — over 100,000 rules and 10M+ intel entries — into validated results, not noise.
Binary & memory scanning.
Behavioral analysis of attacker tactics.
Environment-specific detection logic.
Global threat intel core.
Detection, validation, and investigation orchestration inside Defensium.
High-confidence findings instead of false positives.
Threat output visible within minutes.
Readable conclusions instead of raw log pages.
Operation-ready output, ready for action.
An 80M+ verified-hash whitelist minimizes the false-positive rate before an analyst ever sees an alert.
Atlantis is Defensium's forensic engine — it acquires, indexes, parses and correlates endpoint evidence into an investigation you can defend.
Forensic artifact acquisition from endpoints.
Fast retrospective search across collected data.
Collected data rendered in readable form.
Relationships between artifacts, events and hosts.
Investigation driven by timeline and evidence.
MFT, Registry, Event Logs, Browser History, Shimcache/Amcache, Memory Dumps and far more, out of the box.
Point Defensium at a file path and it collects it — targeted, custom log collection via triage.
Telemetry pulled from the host strengthens investigation context through timeline and correlation.
When evidence, detection and response stay together, analysts validate faster without rebuilding context.
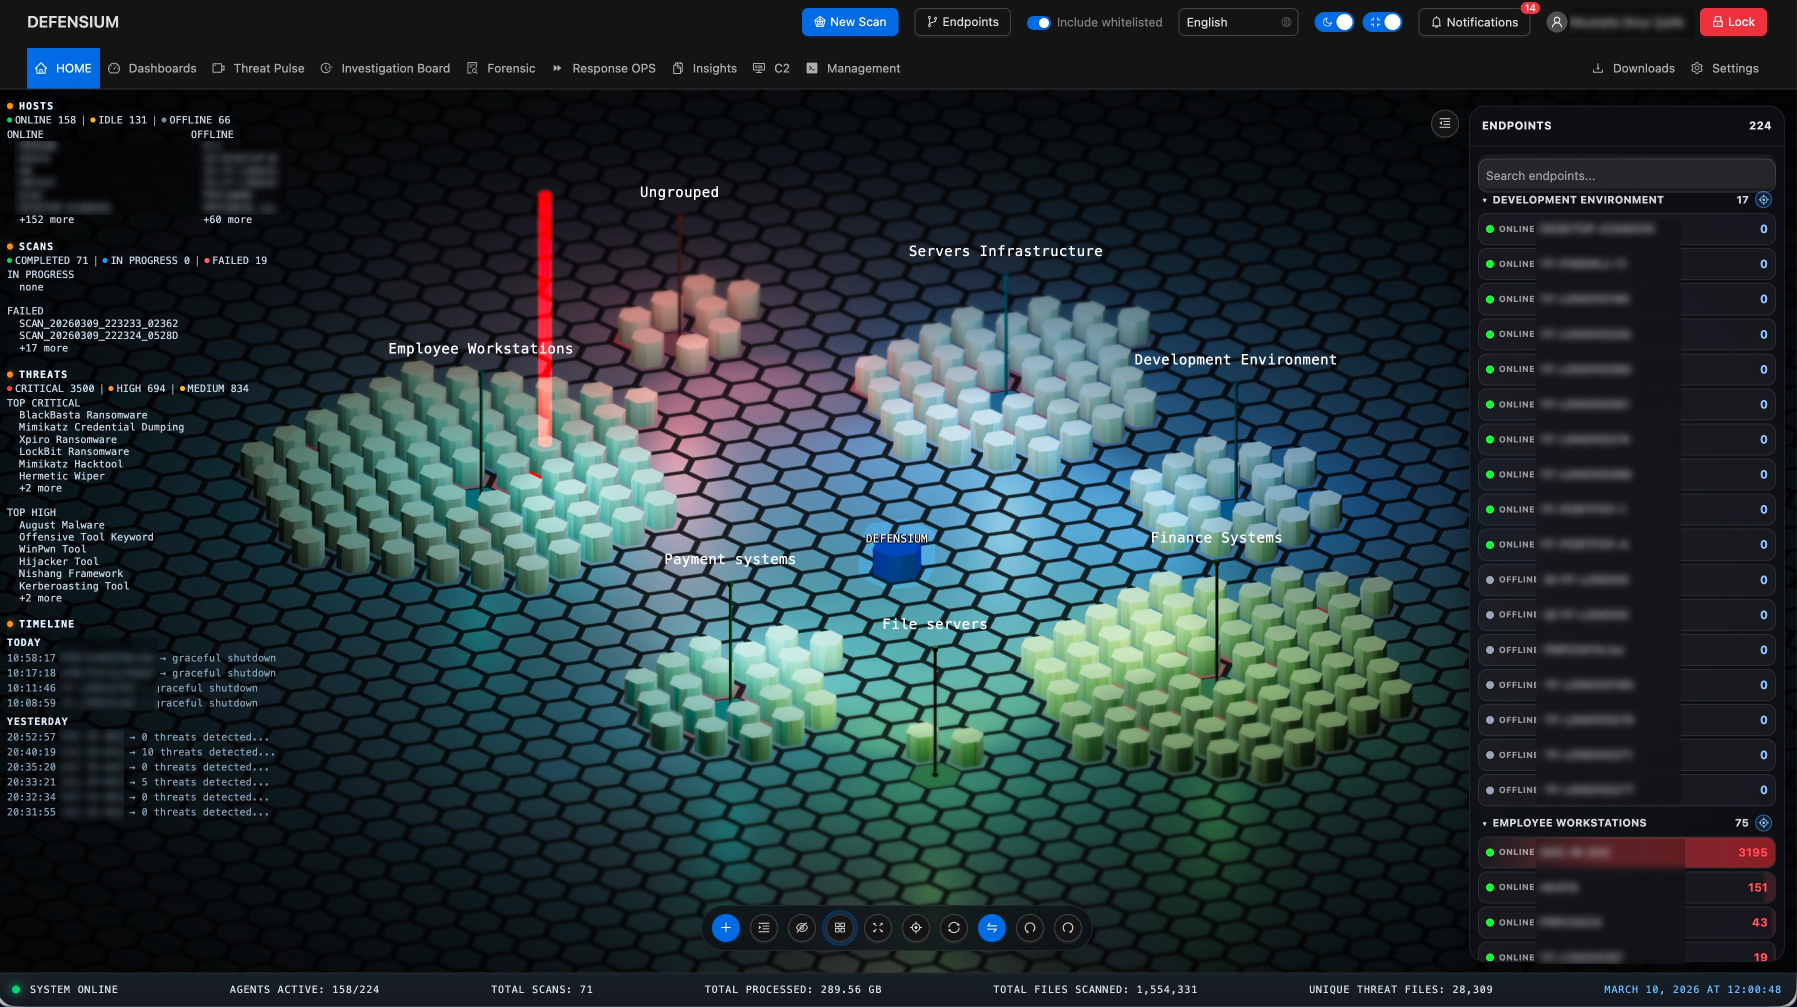
A clustered 3D map exposes environment segments, host density and blast-radius context at a glance.
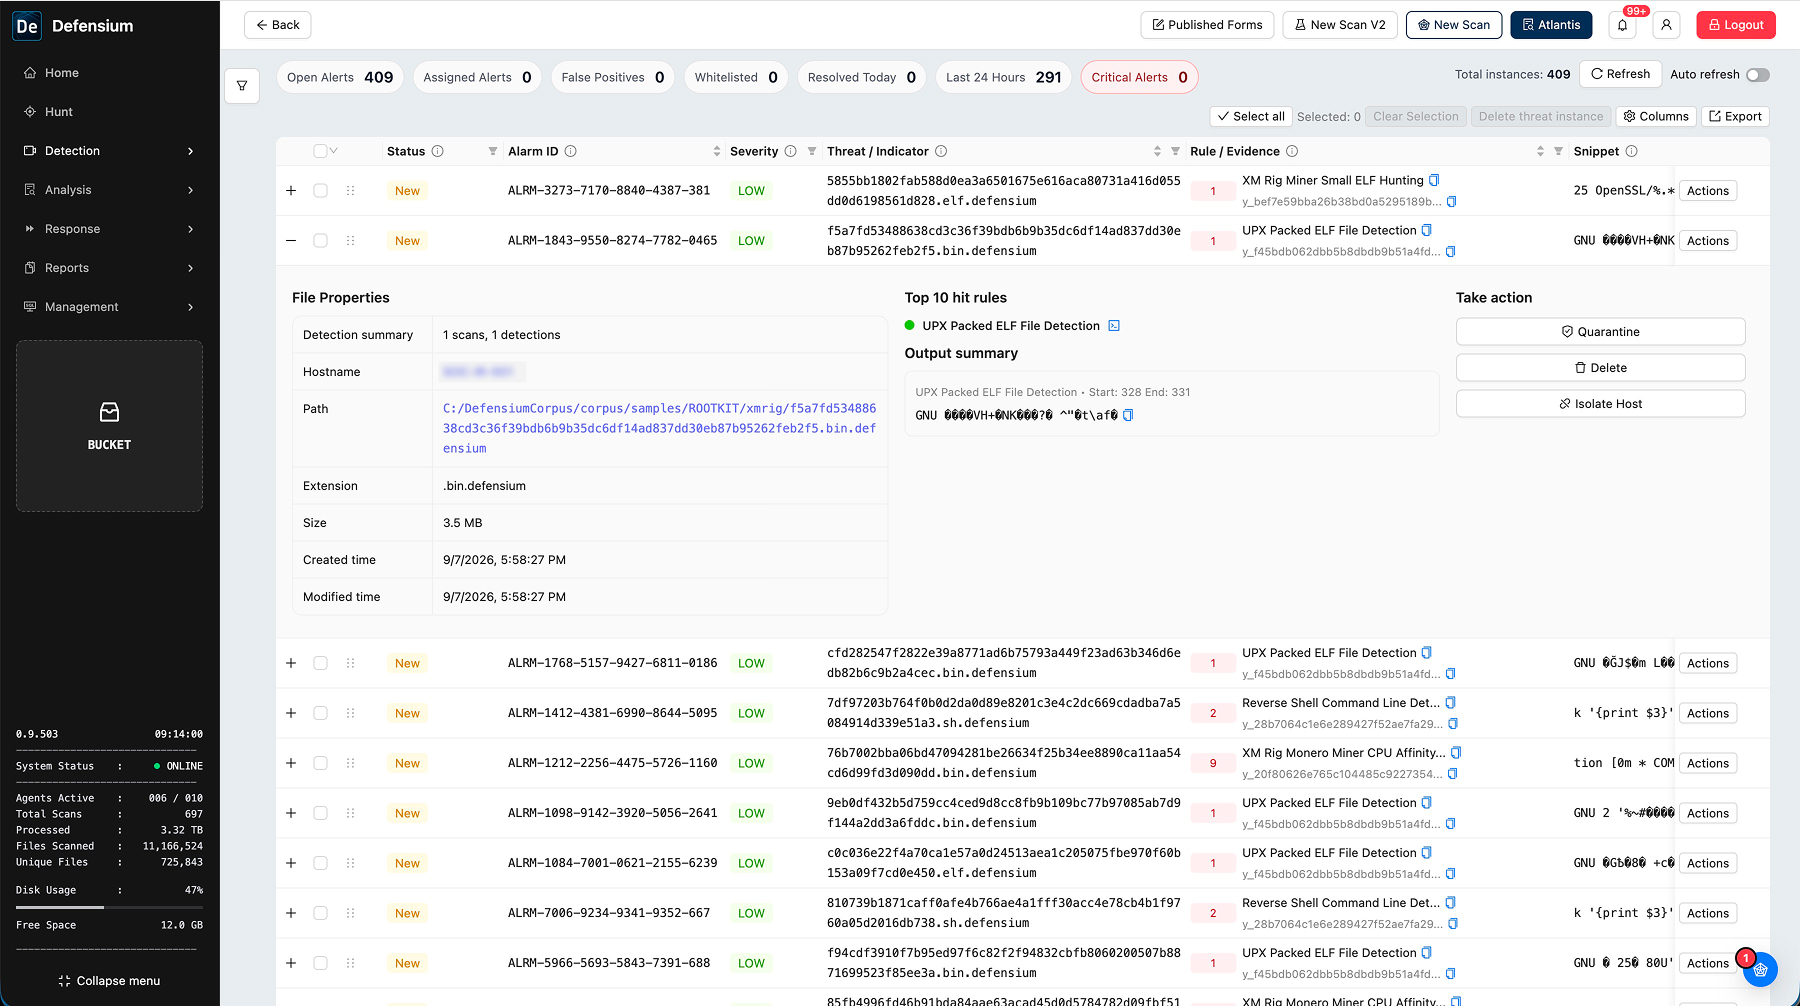
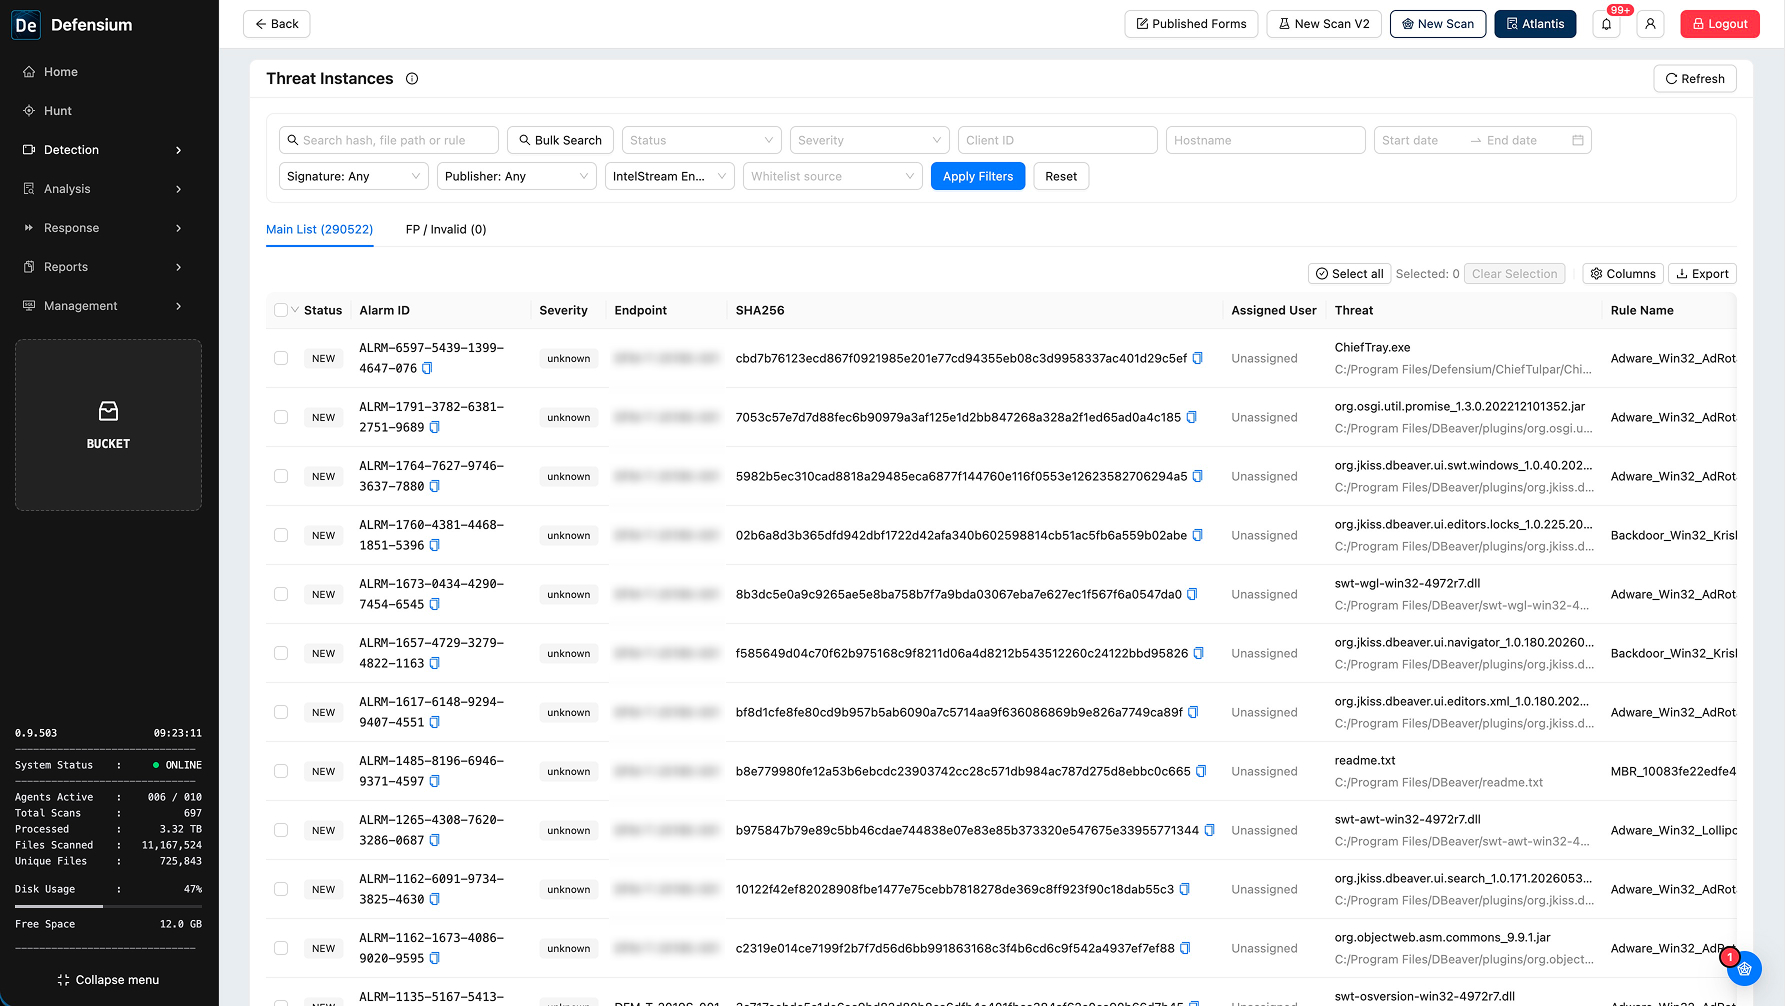
Threat list, severity, evidence and response actions in one surface — a shorter triage path with built-in actions.
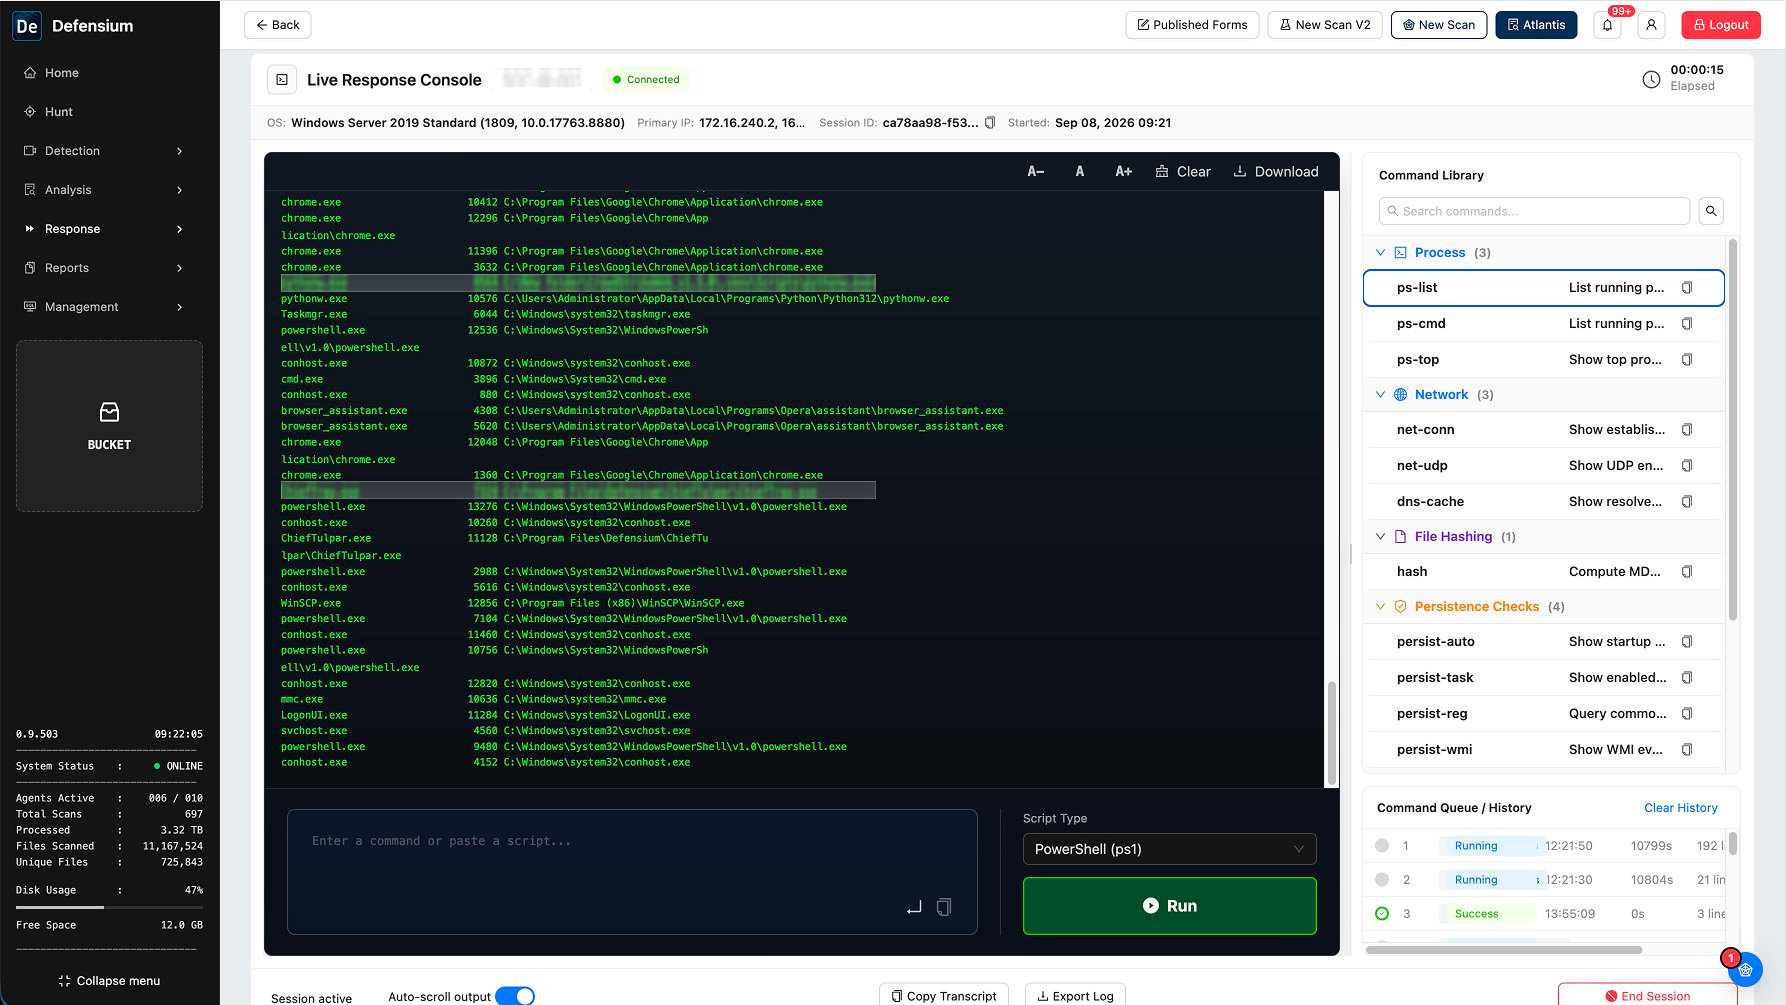
Live shell, command library and case-linked history bring containment into the same response flow.
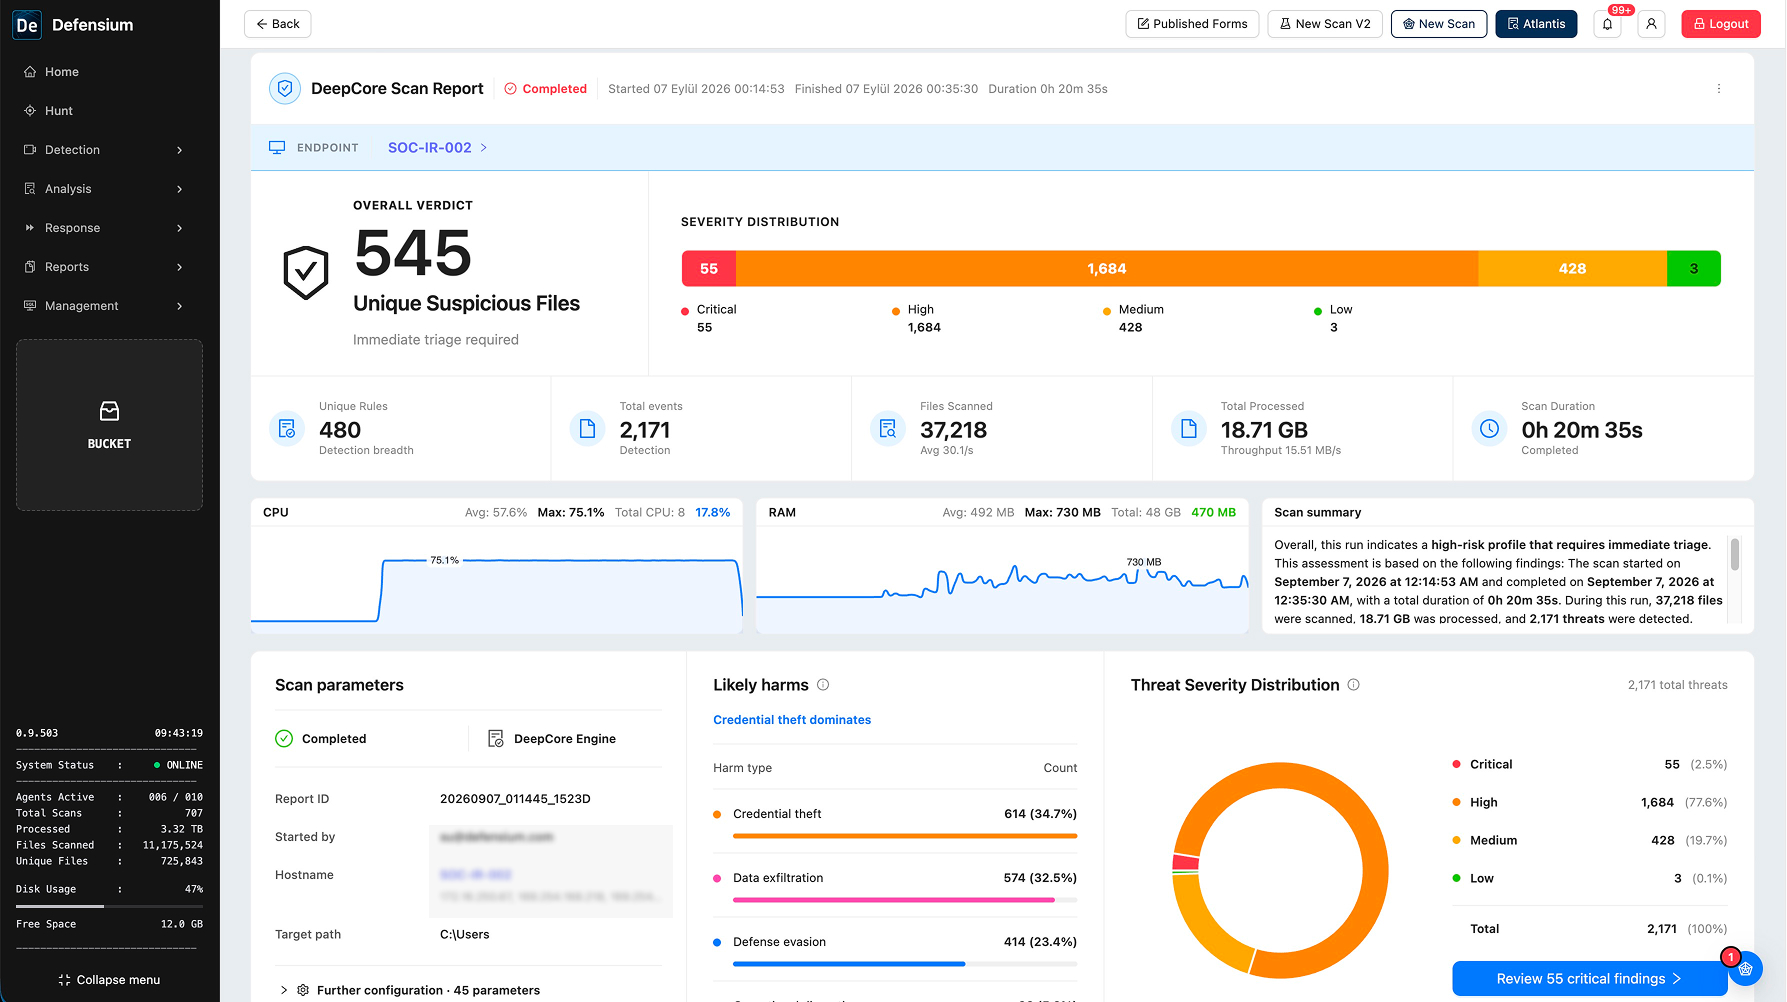
Scan summary, severity distribution, MITRE ATT&CK context and IOC coverage in one reporting surface — executive-readable and analyst-grade.
Raw event access, filtering and grouped evidence let analysts move from summary findings into deep inspection without changing tools.
Defensium keeps response decisions tied to the context of the investigation; teams act on evidence, not guesswork. Analysts can take action on thousands of hosts with a single button using the operations center.
Cut host communication and limit lateral movement.
Block malicious files, hashes, paths or indicators.
Take a shell on the machine and run host queries for rapid intervention and visibility.
Quarantine, block, allow or transfer files; terminate processes; stop or delete services; remove registry entries and scheduled tasks; disable accounts; and maintain a complete audit trail.
Run standardized response workflows automatically.
Investigation output and operational control live on the same platform — no export-and-stitch between tools.
Defensium brings high scan performance, low resource consumption and deep detection / DFIR capability together on a single agent.
Typical consumption on a 48 GB machine — small enough for your most critical servers.
Apply a CPU cap so system balance is preserved even during high-performance scans.
10 GB of data scanned against 100,000+ rules and 1M intel entries in about seven minutes.
Scanning speed and low footprint combined with full DFIR capability on one platform.
What enterprise teams actually need to move from signal to outcome.
Designed for organizations that require complete data control and distribution flexibility.
Run inside your environment; no investigation data routed through third parties.
Evidence handling and analysis stay inside your security boundary.
A fit for regulated sectors, critical infrastructure and high-trust environments.
Deployment models built for tighter control over data locality and handling.
Each license is priced per agent, so you scale with your fleet — start with what you need and grow into the full platform.
DFIR-focused.
Detection & validation-focused.
The complete platform.
Threat research, real-world use cases, technical documentation and the integration roadmap — everything a buyer, analyst or integrator needs to evaluate the platform.
Detection notes, DFIR walkthroughs, compromise-assessment findings and product updates from the Defensium team.
Read →How teams put Defensium to work for compromise assessment, incident response and proactive threat hunting.
Explore →Architecture, deployment, supported artifact categories, MITRE ATT&CK coverage and the API reference — the full evaluation detail.
Explore →SIEM, SOAR, EDR and XDR integrations plus an open API — so Defensium plugs into the tools you already run.
Coming soonBook a tailored walkthrough to see how Defensium helps security teams detect, investigate, and respond faster.
Enterprise workflows. Privacy-first deployment. Technical depth built for serious security teams.